Offensive securityfor teams thatship fast and stay compliant.

Continuous penetration testing, red team operations, and product security engineering, delivered by operators through a live findings platform. Not a once-a-year PDF.

0+
Engagements
0
CVEs disclosed
0d
Median kickoff
24/7
Findings stream

Independent expertise

Trusted by industry leaders

The credentials, programs, and communities that shape how our operators work.

View credential details

Accreditations

Credentials & frameworks

OSDA OffSec badgeOSWE OffSec badgeOSWA OffSec badgeOSCP+ OffSec badgeOSED OffSec badgeOSEP OffSec badgeOSCE³ OffSec badgeGIAC OffSec badgeZero-Point Security OffSec badgeOWASP OffSec badgeMITRE OffSec badgeNIST OffSec badgePTES OffSec badgeOSSTMM OffSec badge

Hall of fame

Public security programs & disclosure

Bugcrowd OffSec badgeHackerOne OffSec badgeGoogle VRP OffSec badgeMicrosoft MSRC OffSec badgeApple Security OffSec badgeMeta Bug Bounty OffSec badgeDoD VDP OffSec badgeNASA VDP OffSec badgeGitHub Security Lab OffSec badge

Conferences

Research and practitioner communities

Black Hat OffSec badgeDEF CON OffSec badgeNullcon OffSec badgeOWASP AppSec OffSec badgeBSides OffSec badgeFIRST OffSec badgeHITBSecConf OffSec badgePOC OffSec badge

Credentials are held by individual practitioners.

Services

Full-coverage offensive security - on a retainer, not a PO cycle.

One team. Seven practices. Delivered through a shared findings platform so you can prioritize, assign, and retest without leaving the tool you already use.

Findings platform

Your security program, without the PDF lag.

Every finding, PoC, retest, and auditor-facing artifact in one live view. Wired to Jira, Linear, GitHub, and Slack so the team that needs to fix it never leaves their tool.

Inside the platform

From confirmed finding to developer-ready remediation, without the PDF handoff.

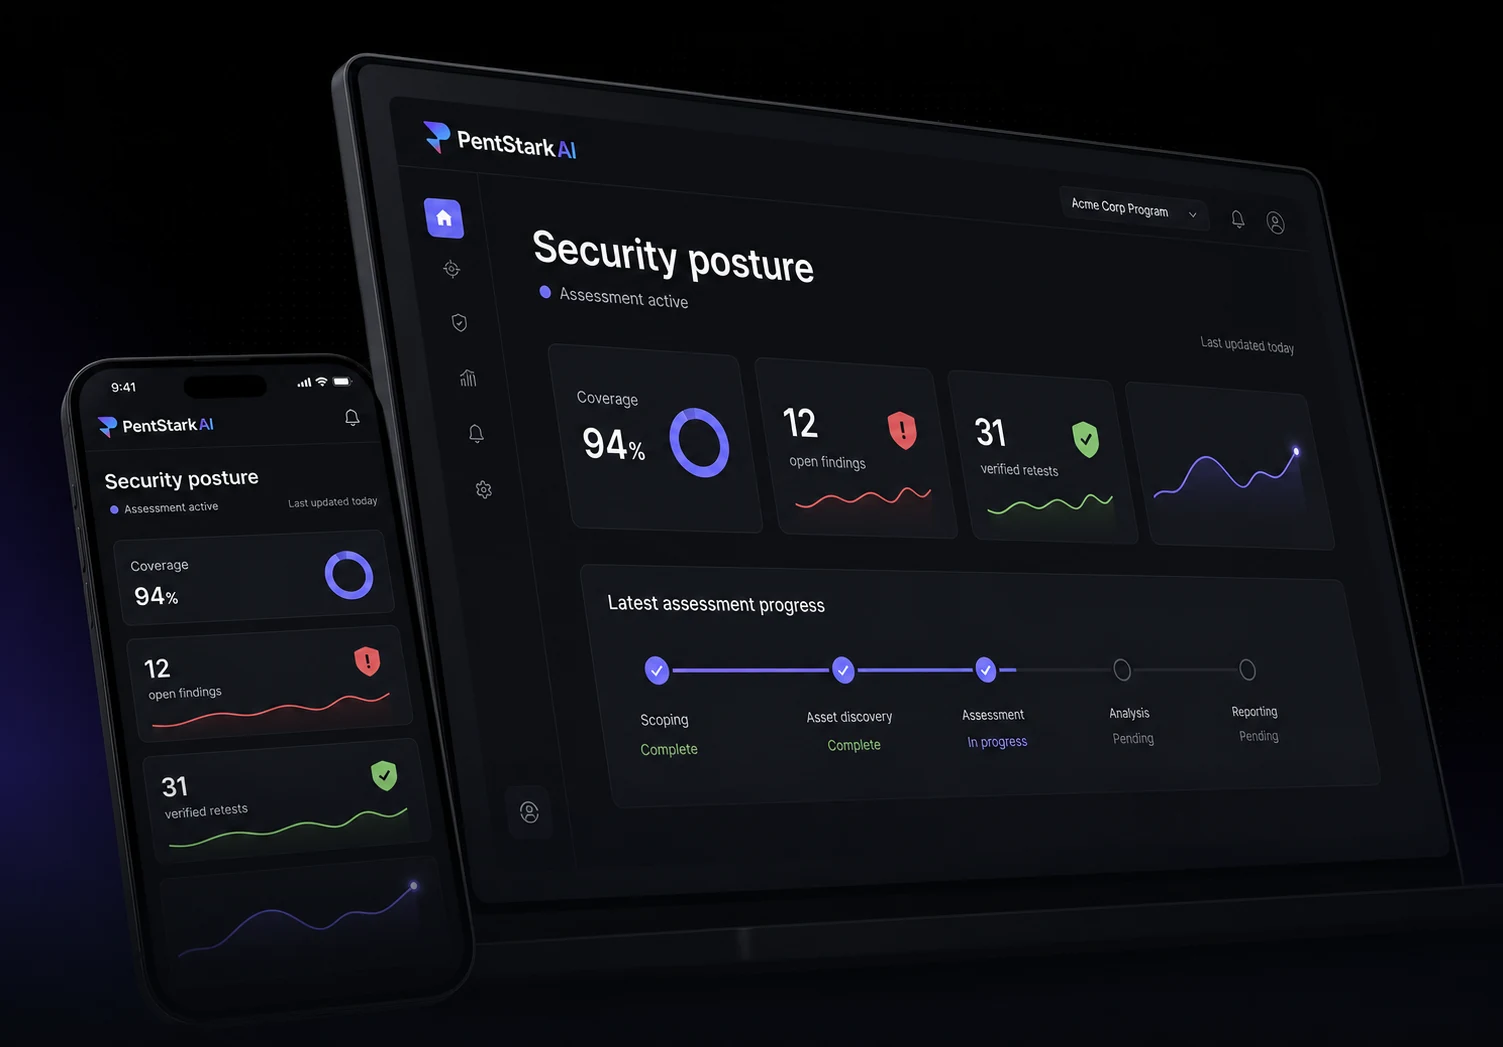
PentStark Security posture dashboard displayed on desktop and mobile devices

See your security posture at a glance

Track coverage, open findings, verified retests, and assessment progress across every screen.
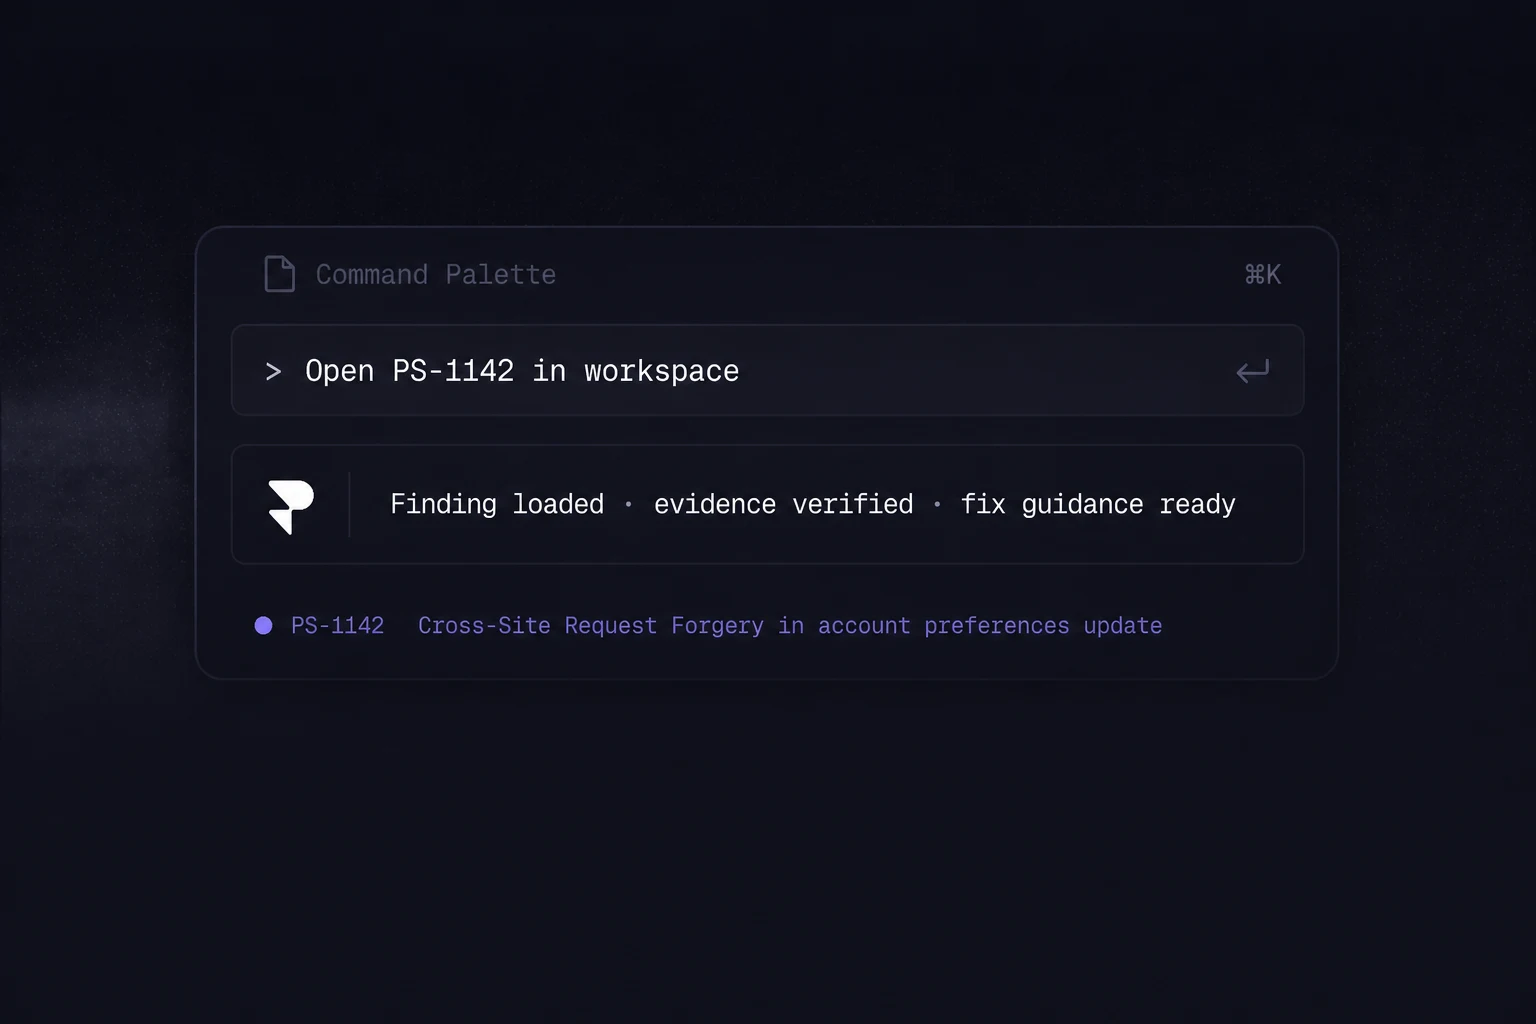
Integrations that fit your workflow

One-way or two-way sync with Jira, Linear, GitHub Issues, Azure DevOps, Slack, Teams, PagerDuty.

Evidence your auditor accepts

Export SOC 2 / ISO 27001 / PCI-DSS-aligned artifacts with reproducible PoCs attached.

Live retest, not annual redo

Re-verification within 5 business days of fix - unlimited within the engagement window.

Methodology

How we work - open, reproducible, auditable.

Every engagement maps to published frameworks (PTES, OWASP WSTG / MASVS, OSSTMM, NIST SP 800-115, MITRE ATT&CK) so your auditors and engineers see the same story.

Phase 01

Scoping

Objectives, rules of engagement, threat model, success criteria.

Output / Signed SOW + ROE
Phase 02

Reconnaissance

Attack-surface discovery, asset graph, exposure scoring.

Output / Asset graph
Phase 03

Exploitation

Manual + tooled exploitation aligned to PTES, OWASP, MITRE ATT&CK.

Output / Kill-chain log
Phase 04

Reporting

Developer-grade writeups with reproduction, PoC, CVSSv4, and fix guidance.

Output / Finding + PoC
Phase 05

Remediation

Paired work with your engineering team; retests at no extra cost.

Output / Fix PR + retest
Phase 06

Continuous

Findings platform, weekly syncs, delta-retests on every release.

Output / Live dashboard
MITRE ATT&CK coverage

A clear view of every path an attacker can take.

We map each engagement to Enterprise tactics, techniques, and sub-techniques - then turn the paths we find into atomic tests your team can replay.
Enterprise matrix
Techniques + sub-techniques in scope
42 mapped paths
01
Initial Access
How an adversary gets in
T1566
Phishing
T1566.001
Spearphishing Attachment
T1566.002
Spearphishing Link
T1190
Exploit Public-Facing Application
T1078.004
Valid Accounts: Cloud Accounts
02
Execution
Running malicious code
T1059
Command and Scripting Interpreter
T1059.001
PowerShell
T1059.003
Windows Command Shell
T1059.009
Cloud Shell
T1204.002
User Execution: Malicious File
03
Persistence
Staying in the environment
T1053.005
Scheduled Task/Job: Scheduled Task
T1098.001
Account Manipulation: Additional Cloud Roles
T1505.003
Server Software Component: Web Shell
T1136.003
Create Account: Cloud Account
04
Privilege Escalation
Reaching a higher level of access
T1548.002
Bypass User Account Control
T1068
Exploitation for Privilege Escalation
T1134.001
Access Token Manipulation: Token Impersonation
T1548.005
Temporary Elevated Cloud Access
05
Defense Evasion
Avoiding detection and controls
T1070.004
Indicator Removal: File Deletion
T1562.001
Impair Defenses: Disable or Modify Tools
T1027.002
Obfuscated/Compressed Files: Software Packing
T1218
System Binary Proxy Execution
06
Credential Access
Stealing secrets and identities
T1003.001
OS Credential Dumping: LSASS Memory
T1555.003
Credentials from Web Browsers
T1110.001
Brute Force: Password Guessing
T1552.001
Unsecured Credentials: Credentials In Files
07
Discovery
Learning what is worth targeting
T1087.002
Account Discovery: Domain Account
T1049
System Network Connections Discovery
T1526
Cloud Service Dashboard
T1018
Remote System Discovery
08
Lateral Movement
Moving between systems and tenants
T1021.001
Remote Services: RDP
T1021.002
Remote Services: SMB/Windows Admin Shares
T1550.002
Use Alternate Authentication Material: Pass the Hash
T1570
Lateral Tool Transfer
09
Collection & C2
Gathering data and controlling the foothold
T1213
Data from Information Repositories
T1114.002
Email Collection: Remote Email Collection
T1071.001
Application Layer Protocol: Web Protocols
T1105
Ingress Tool Transfer
10
Exfiltration & Impact
Taking action on the objective
T1041
Exfiltration Over C2 Channel
T1567.002
Exfiltration Over Web Service: Cloud Storage
T1486
Data Encrypted for Impact
T1490
Inhibit System Recovery
Representative portrait for an anonymized fintech engineering leader

Series C fintech · Singapore

VP Engineering

“Pentstark's PTaaS retainer replaced three vendors for us. Findings land in Linear the same hour they are found, and the retest cadence finally matches how we ship.”

Measured outcome

MTTR reduced from 11 days to 3

Why teams pick us

A partner your security, engineering, and compliance teams can all point to.

Credentials

Operator credentials

Team-held credentials include OSCP, OSCE³, OSWE, CRTO, CISSP, CCSP, GXPN, and GPEN.

OSCPOSCE³OSWECRTOCISSP
Individual credentials available on request
Data handling

Confidentiality first

Findings encrypted in transit and at rest. Per-engagement data segregation. Signed mutual NDA and DPA.

E2E encryptedDPA · NDA
Applied to every engagement
Delivery standard

Open methodology

PTES, OWASP WSTG / MASVS, OSSTMM, NIST SP 800-115, MITRE ATT&CK mapped on every engagement.

PTESOWASPMITRE
Mapped in every report
Research record

Published research

42 CVEs disclosed responsibly. Regular write-ups, conference talks, and zero-day advisories.

42 CVEsConf talks
Responsible disclosure first
Talk to an operator

Your next finding is one scoping call away.

Thirty minutes with a real operator tells us what you need and what we can deliver. No BDR handoff, no sales engineer theater. The person you talk to is the person who scopes the work.

● Responses in < 1 business day